Quick Answer: The PowerShell Script Installer for Win32 Apps in Microsoft Intune separates deployment scripts from application binaries (.intunewin). To use it, package vendor binaries with the Win32 Content Prep Tool, configure your Win32 app under Apps > Windows, and switch the install type from Command line to PowerShell script. You can then upload, view, and edit installation and uninstallation scripts directly in the Intune console without repackaging or re-uploading large application files.
What Is the PowerShell Script Installer for Win32 Apps in Intune?
The PowerShell Script Installer for Win32 Apps is a native capability in Microsoft Intune that allows administrators to upload and manage application installation and uninstallation PowerShell scripts directly within the Intune admin console. This feature separates deployment scripting logic from the packaged .intunewin binary payload, eliminating the traditional requirement to re-wrap and re-upload large application source packages when adjusting script logic.
Historically, deploying desktop applications through Microsoft Intune required packaging both the vendor binaries and the orchestration script (such as Deploy-Application.ps1 from the PSAppDeployToolkit) into a single encrypted .intunewin file using the Microsoft Win32 Content Prep Tool. If you needed to update a detection registry key, alter a command-line argument, or insert a pre-flight prerequisite check, you had to re-run the preparation tool and upload the entire multi-gigabyte payload back to Microsoft cloud storage.
With the release of native script installer support, Intune separates the installation logic from the application media. You upload your core software binaries inside a static .intunewin wrapper once, while dynamically configuring your installation script, uninstallation script, and execution parameters directly in the Intune portal.
When deploying a 2GB software suite like Autodesk, MATLAB, or Visual Studio, updating installation switches or post-install registry fixes previously took 45 minutes of repackaging and bandwidth-heavy uploads. With the PowerShell script installer, you update the script in the portal in 10 seconds. The Intune Management Extension then runs the new script against the cached payload on client devices automatically.
,
Traditional Win32 Wrapping vs. Native PowerShell Script Installer
Understanding how the architectural boundary shifts between traditional Win32 app packaging (.intunewin wrappers) and the native script installer explains why this feature is essential for modern enterprise endpoint management:
| Operational Dimension | Traditional Win32 App Packaging | Native PowerShell Script Installer |
|---|---|---|
| Script Location | Embedded inside encrypted .intunewin container. | Uploaded & managed directly in Intune Admin Center. |
| Binary Maintenance | Repackaging required for any minor script modification. | Binary container remains untouched; scripts update instantly. |
| Bandwidth & Upload Impact | Full re-upload of application files (e.g., 500MB to 15GB). | Zero bandwidth waste because only the lightweight .ps1 script gets updated. |
| Script Signature Enforcement | Requires custom wrapper code or GPO certificate validation. | Native Intune portal checkbox: Enforce script signature check. |
| Architecture Context | Requires command line prefix (powershell.exe -ExecutionPolicy Bypass). | Native toggle for Run script as 32-bit process on 64-bit clients. |
| Logging Standard | Must manually redirect standard out (*> log.txt). | Integrated Intune Management Extension (IME) agent execution tracking. |
,
Prerequisites and System Requirements
Before implementing the native script installer for enterprise production workloads, verify that your tenant and client endpoints meet the following environmental requirements:
- Microsoft Intune Service Release: Tenant running Service Release 2601 or higher.
- Operating System Support: Windows 11 (Home, Pro, Enterprise, Education) or Windows 10 (version 1607 and later).
- Intune Management Extension (IME): Active IME agent installed on the endpoint (provisions automatically upon initial Intune enrollment).
- PowerShell Version: Windows PowerShell 5.1 (default) or PowerShell 7.x (if configured on the host).
Administrative Privileges: Intune Administrator, Cloud Device Administrator, or custom RBAC role with Device Apps / Read & Create* permissions.
,
Step-by-Step Implementation Guide (Real-World Example: Google Chrome)
You can utilize the native PowerShell Script Installer in two distinct scenarios:
> 1. Creating a Brand-New App: When onboarding fresh software, upload your minimal .intunewin payload and configure the script installer directly under the Program step during creation.
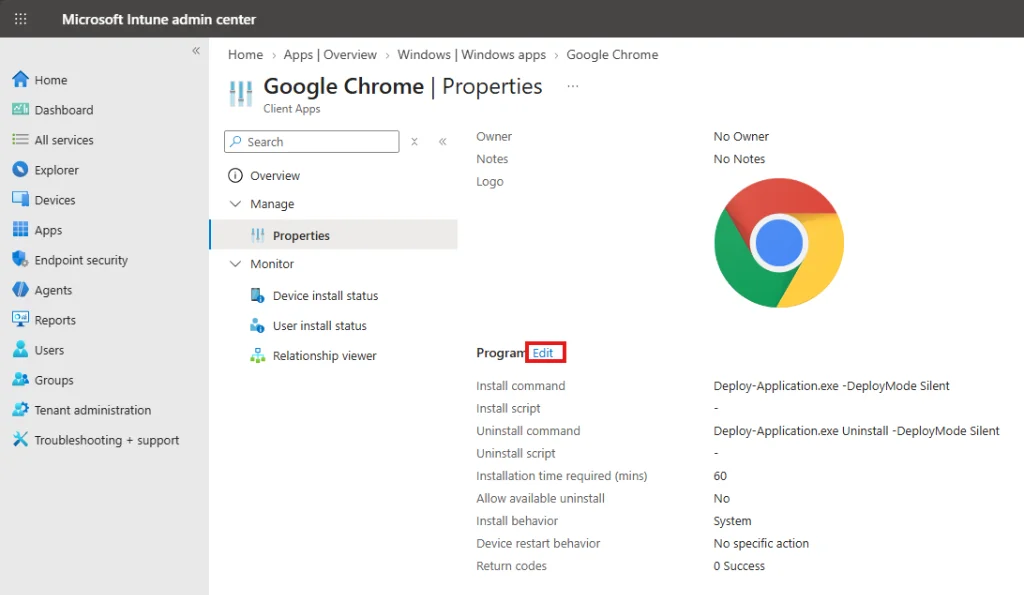
> 2. Modifying an Already Created App: If you have existing Win32 apps deployed via traditional command lines, you do not need to recreate them from scratch. Open the existing app’s Properties, click Edit next to Program, and switch the installer type directly to PowerShell script.
To illustrate the complete end-to-end lifecycle, we will package and deploy Google Chrome Enterprise:
– Application Payload: googlechromestandaloneenterprise64.msi
– Installation Orchestration: Install.ps1 (with dynamic $PSScriptRoot resolution)
– Uninstallation Orchestration: Uninstall.ps1
,
Step 1: Create the Minimal Application Payload
Even though the orchestration script is managed independently, Intune still requires an .intunewin container to store the software installer binaries (vendor MSI, EXE, or support files).
- Create a staging folder on your technician workstation:
C:PackagesChromeSource. - Place
googlechromestandaloneenterprise64.msiinto the folder. Do not place your installation orchestration script here. - Open terminal and run the Microsoft Win32 Content Prep Tool (
IntuneWinAppUtil.exe):
CMD • IntuneWinAppUtil Packaging
POWERSHELL • Install-GoogleChrome.ps1
<#
.SYNOPSIS
    Enterprise Win32 Application Installation Wrapper for Intune Native Script Installer
.DESCRIPTION
    Executes vendor setup in SYSTEM context, logs output to IME directory, and returns proper exit codes.
#>

[CmdletBinding()]
param()

# Setup Logging to Intune Management Extension Directory
$LogPath = "$env:ProgramData\Microsoft\IntuneManagementExtension\Logs"
if (-not (Test-Path -Path $LogPath)) {
    New-Item -Path $LogPath -ItemType Directory -Force | Out-Null
}
$LogFile = Join-Path -Path $LogPath -ChildPath "AppDeploy_Install.log"
Start-Transcript -Path $LogFile -Append -Force

try {
    Write-Host "[INFO] Initiating deployment via native Intune PowerShell Script Installer..." -ForegroundColor Cyan
    $SourceDir = $PSScriptRoot
    $Installer = Join-Path -Path $SourceDir -ChildPath "googlechromestandaloneenterprise64.msi"

    if (-not (Test-Path -Path $Installer)) {
        throw "Payload binary not found at path: $Installer"
    }

    Write-Host "[INFO] Executing vendor installer silently..."
    $Arguments = "/i `"$Installer`" /qn /norestart ALLUSERS=1"
    $Process = Start-Process -FilePath "msiexec.exe" -ArgumentList $Arguments -Wait -PassThru -NoNewWindow

    Write-Host "[INFO] Process finished with Exit Code: $($Process.ExitCode)"

    # Evaluate Exit Codes (0 or 3010)
    if ($Process.ExitCode -eq 0 -or $Process.ExitCode -eq 3010) {
        Write-Host "[SUCCESS] Application deployed successfully." -ForegroundColor Green
        Stop-Transcript
        exit $Process.ExitCode
    } else {
        Write-Warning "[ERROR] Vendor installer returned failure exit code: $($Process.ExitCode)"
        Stop-Transcript
        exit $Process.ExitCode
    }
}
catch {
    Write-Error "[FATAL] Script failure: $($_.Exception.Message)"
    Stop-Transcript
    exit 1
}
,
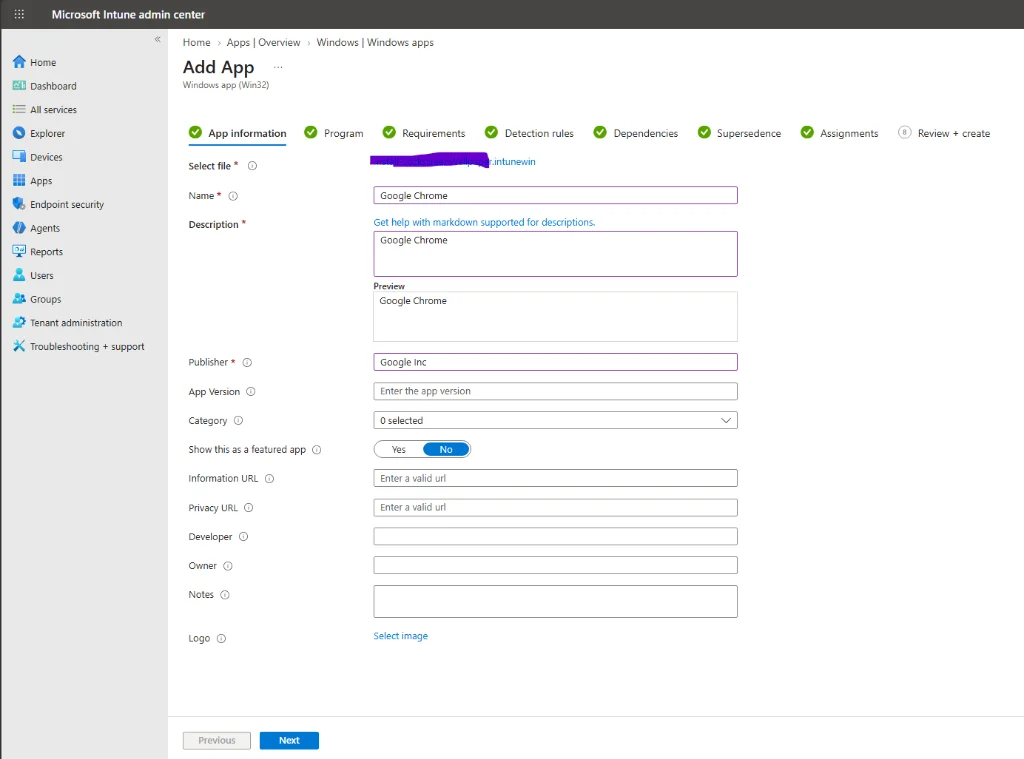
Step 2: Add a New Win32 App in Intune (or Edit an Existing Deployment)
When onboarding a new package, upload your newly wrapped .intunewin payload and fill out the initial catalog details:
- Sign in to the Microsoft Intune admin center.
- Go to Apps > Windows > Windows apps and click + Add.
- Under App type, select Windows app (Win32) and click Select.
- Select your
googlechromestandaloneenterprise64.intunewinpackage file and complete the App information fields (Name, Description, Publisher, and Version):
If you already have Google Chrome or another Win32 application deployed in your tenant, you do not have to create a new package. Open your existing app’s Properties, scroll down to Program, and click Edit to switch over to the PowerShell script installer without disrupting assigned users.
Step 3: Select the PowerShell Script Installer Type
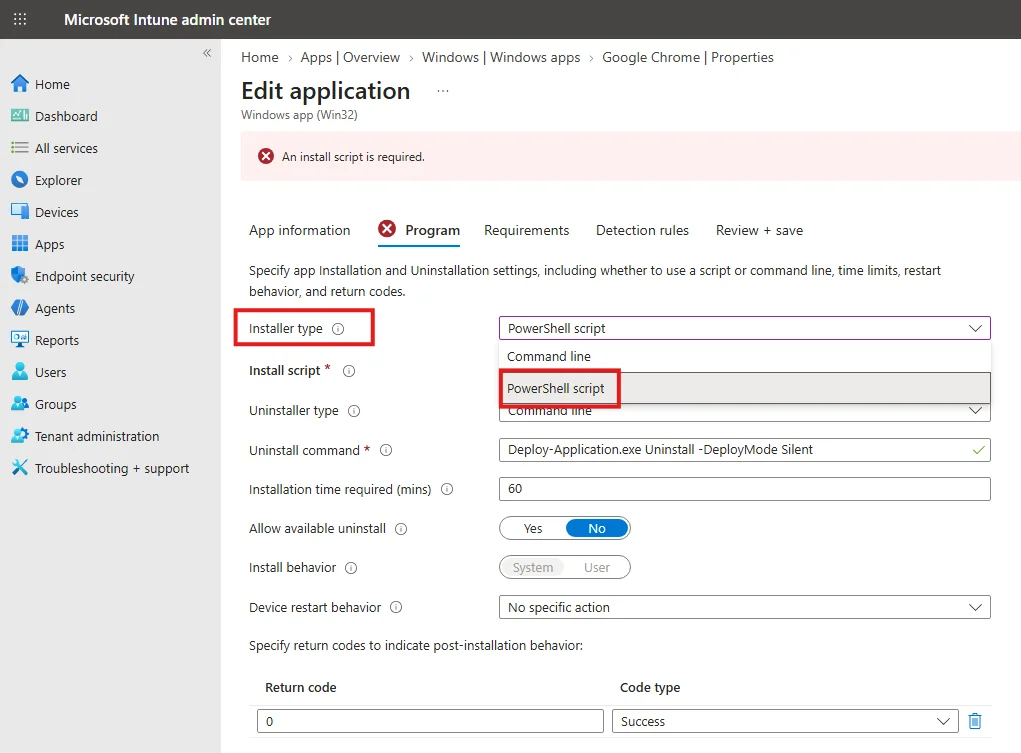
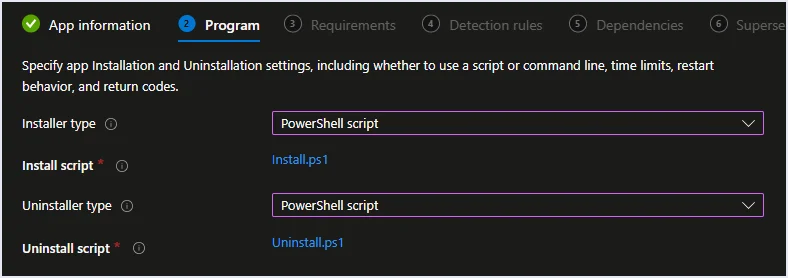
- In the Program settings blade, locate the Installer type dropdown.
- Change the selection from Command line to PowerShell script:
,
Step 4: Upload Deployment Scripts & Configure Execution Controls
- Upload your separate
Install.ps1andUninstall.ps1files:
– Install script: UploadInstall.ps1.
– Uninstaller type: Select PowerShell script and uploadUninstall.ps1.
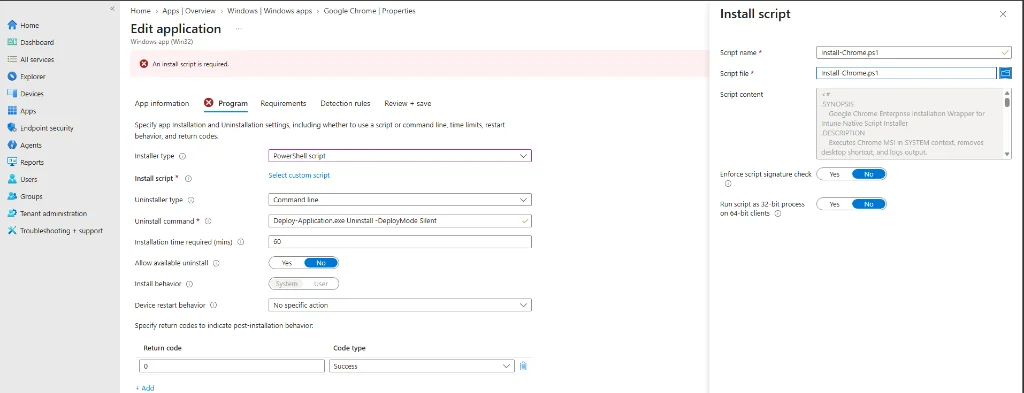
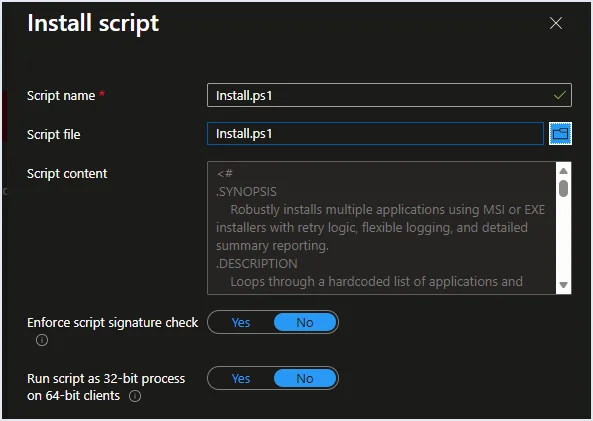
- Click on the script file to configure execution options in the flyout blade:
– Enforce script signature check: Toggle to Yes if enforcing PKI code-signing certificates; otherwise No.
– Run script as 32-bit process on 64-bit clients: Set to No (runs in native 64-bit PowerShell host).
Step 5: Configure Operating System Requirements
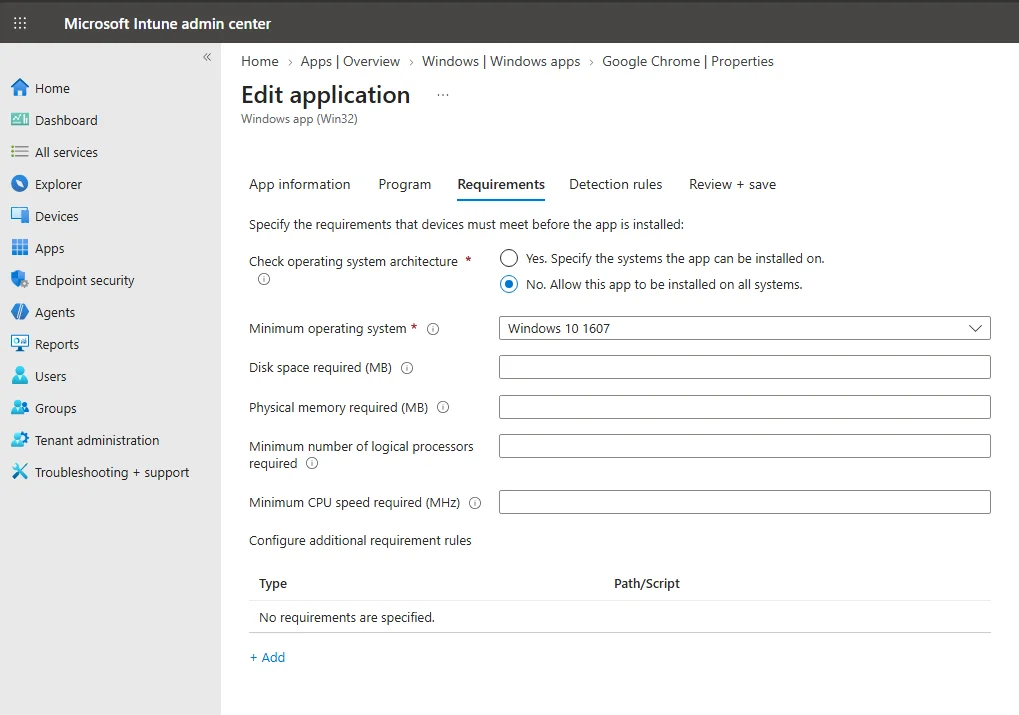
Under the Requirements tab, define the client device specifications necessary before the Intune Management Extension triggers the installer:
- Operating system architecture: Select whether the application targets 32-bit, 64-bit, or all architectures (set to 64-bit for Google Chrome 64-bit Enterprise).
- Minimum operating system: Select the baseline Windows version (e.g., Windows 10 1607 or later).
- Optional hardware rules: Specify disk space, physical memory, or custom requirement script checks if applicable.
Step 6: Configure Accurate Detection Rules (MSI & Script)
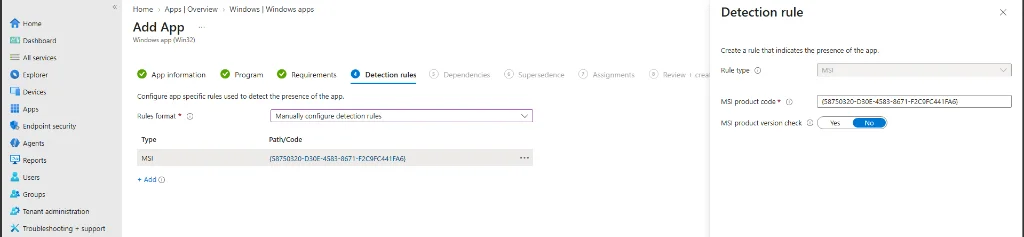
The Intune Management Extension checks detection rules immediately after the script installer finishes execution. If the rule evaluates to false, Intune reports an installation failure even if the installer exited with code 0.
When deploying MSI packages like Google Chrome, configure an MSI Detection Rule:
- Under Rules format, select Manually configure detection rules.
- Click + Add and set Rule type to MSI.
- The MSI product code GUID is automatically populated from your package metadata (e.g.,
{58750320-D30E-4583-8671-F2C9FC441FA6}). - Set MSI product version check to No (or Yes to enforce a specific build version comparison).
Step 7: Review Dependencies & Supersedence (Optional)
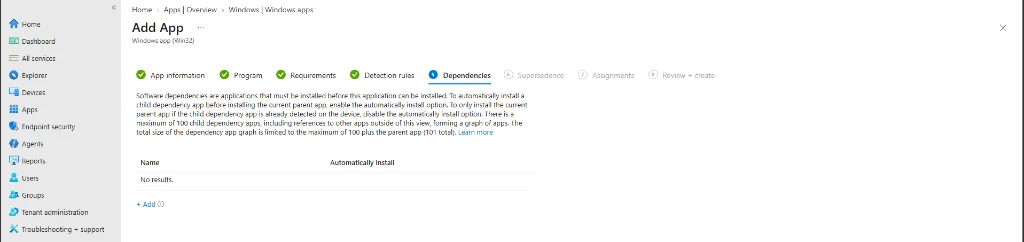
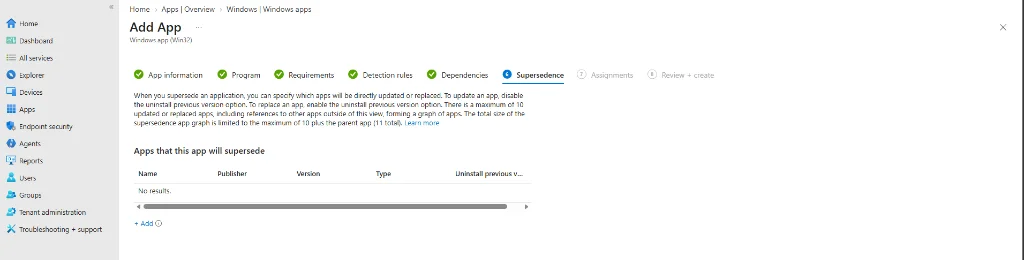
Most enterprise software installs cleanly on its own. If your software needs prerequisites, Intune handles them through these two optional screens:
- Dependencies: Software dependencies are prerequisites that must install prior to the parent app (e.g., Visual C++ Redistributable or .NET Runtime). If no prerequisites are required, leave as No results.
- Supersedence: When upgrading or replacing older browser builds or legacy software, configure supersedence chains here. For fresh standalone deployments, leave this tab blank.
Step 8: Configure Group Assignments & Deploy
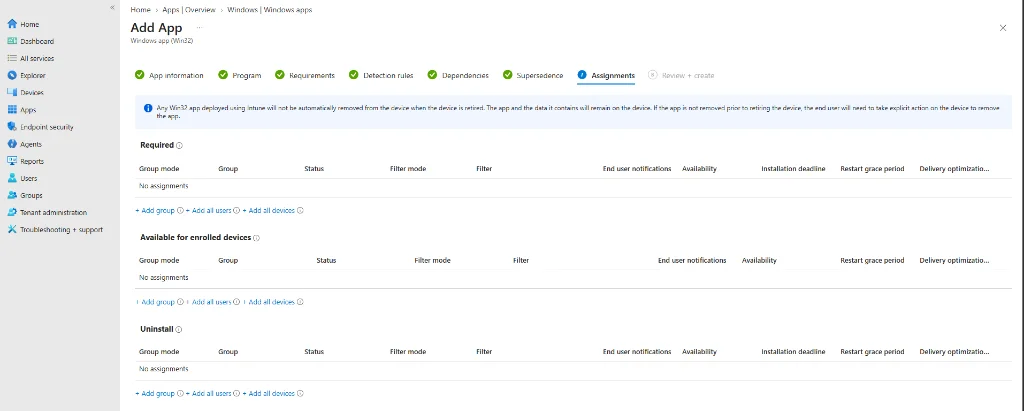
Under the Assignments tab, target the deployment to your corporate user or device groups:
- Required: Enforces automated, silent background installation via the Intune Management Extension on enrolled workstations.
- Available for enrolled devices: Publishes Google Chrome to the Company Portal app, allowing users to initiate on-demand self-service installs.
- Uninstall: Targets endpoints where the software should be cleanly removed using
Uninstall.ps1.
Step 9: Live In-Portal Script Editing (Zero Repackaging)
If you need to adjust installation arguments, update post-install registry keys, or alter configurations later, you never have to re-wrap or re-upload the 115 MB installer. Simply view and modify the code directly within the Intune console:
Step 10: End-to-End Verification in Windows Company Portal
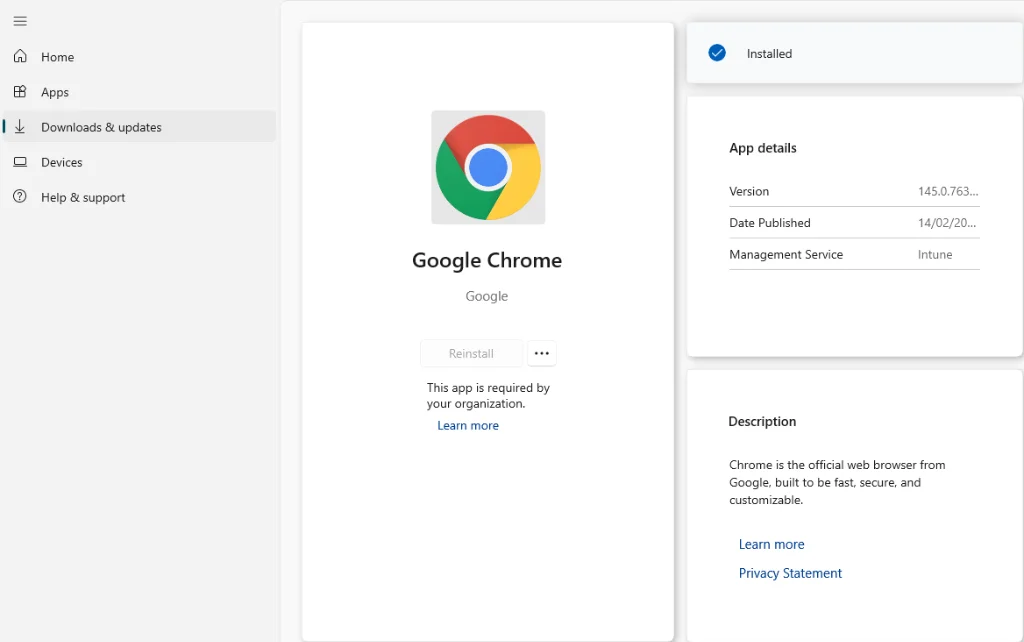
After assigning the app to your target Entra ID device or user group, the endpoint’s Intune Management Extension receives the policy, downloads the package payload, and executes Install.ps1.
Open the Company Portal app on the client workstation to verify end-to-end delivery: navigate to Downloads & updates and confirm that Google Chrome completes smoothly and transitions to Installed:
Production-Grade PowerShell Installer Wrapper
When running under Intune’s NT AUTHORITYSYSTEM account, standard interactive cmdlets will hang indefinitely. Production scripts require explicit working-directory resolution, structured logging compatible with CMTrace, and deterministic return codes.
Use the following enterprise template for your installation script:
Always use $PSScriptRoot to locate installation media. When the Intune Management Extension downloads the application package, it unpacks the content into a temporary GUID folder inside C:Program Files (x86)Microsoft Intune Management ExtensionContent.... Referencing $PSScriptRootgooglechromestandaloneenterprise64.msi guarantees that your binaries are found regardless of where IME caches the files.
,
Troubleshooting Intune Management Extension Logs and Exit Codes
When an application deployed via the PowerShell Script Installer fails, inspect the client diagnostic logs directly on the endpoint.
Key Log Files to Review
IntuneManagementExtension.log: Located inC:\ProgramData\Microsoft\IntuneManagementExtension\Logs. Tracks content download hashes, policy compliance, and whether the installer was triggered.AgentExecutor.log: Contains the execution transcripts of PowerShell scripts executed by the IME agent. Review this file to capture raw standard error output generated during script runtime.- Custom Application Log: As configured in our template above, check
C:\ProgramData\Microsoft\IntuneManagementExtension\LogsAppDeploy_Install.logfor line-by-line script milestones.
Handling Intune Return Codes
By default, Intune maps return codes to installation statuses under Program settings:
* 0 (Success): Application installed cleanly and passed detection.
* 1707 (Success): Successfully completed via internal handler.
* 3010 (Soft Reboot): Success, but system restart required before full functionality.
* 1641 (Hard Reboot): Installer initiated an immediate reboot.
* 1618 (Fast Retry): Another MSI installation is currently in progress. IME retries automatically.
,
People Also Ask (PAA)
Can I update the script without re-uploading the .intunewin file?
Yes. That is the core advantage of the native PowerShell script installer. If you need to fix a script logic bug, alter an argument, or update registry settings, simply edit the app in the Intune admin center, upload the new .ps1 file under the Program tab, and save. Intune redistributes the script to targeted endpoints without downloading the heavy application package again.
Does the PowerShell script run as SYSTEM or User?
It depends on the Install behavior setting selected under the Program tab. If configured as System, the script runs under the NT AUTHORITYSYSTEM account with full elevated administrative privileges. If configured as User, it runs within the security context of the logged-on user.
Do I still need the Microsoft Win32 Content Prep Tool?
Yes. The Microsoft Win32 Content Prep Tool (IntuneWinAppUtil.exe) is still required to package the vendor setup media (such as MSIs, EXEs, and data folders) into an encrypted .intunewin payload. However, you no longer need to package your orchestration script inside that file.
What execution policy does Intune use for the script installer?
The Intune Management Extension automatically launches PowerShell scripts with the -ExecutionPolicy Bypass parameter. This ensures your deployment script executes smoothly even if your tenant or group policy enforces a restrictive execution policy like Restricted or AllSigned.
,
Next Steps in Production
- Package raw vendor binaries into
.intunewinwithout internal scripts. - Switch installer type to PowerShell script in the Intune Program configuration tab (applicable to new or existing apps).
- Upload modular, hardened installation and uninstallation scripts with
$PSScriptRootreferences. - Implement reliable file or registry detection rules that verify the true state of the software.
- Verify end-to-end installation status within the Windows Company Portal app.
- Configure centralized transcript logging into
C:\ProgramData\Microsoft\IntuneManagementExtension\Logsfor rapid troubleshooting.