Quick Answer: To configure Windows LAPS in Intune, enable LAPS under Microsoft Entra ID Device Settings, create a Windows LAPS profile in Intune Endpoint Security Account Protection, and assign the policy to your device group. Windows LAPS automatically generates, rotates, and escrows unique local administrator passwords to Microsoft Entra ID or Active Directory with zero external agents.
What Is Windows LAPS and Why Did It Replace Legacy LAPS?
For more than a decade, systems engineers secured local administrator credentials using legacy Microsoft LAPS. That older solution required deploying an external MSI package (AdmPwd.dll), extending the Active Directory schema, and maintaining Group Policy Objects. It did not support cloud-only Microsoft Entra ID joined endpoints without third-party agents or complex hybrid synchronization scripts.
Modern Windows LAPS is natively integrated into the Windows operating system starting with Windows 10 (20H2, 21H2, 22H2 with the April 2023 cumulative update or later) and Windows 11. It operates through the native Windows operating system kernel, requires no separate client installation, and writes encrypted passwords directly to Microsoft Entra ID or on-premises Active Directory.
| Feature | Legacy Microsoft LAPS | Modern Windows LAPS (Intune) |
|---|---|---|
| Client Software | Requires AdmPwd.dll MSI installer | Built directly into Windows OS kernel |
| Storage Target | On-premises Active Directory only | Microsoft Entra ID or on-premises Active Directory |
| Policy Delivery | Group Policy Objects (GPO) | Microsoft Intune Account Protection CSP or GPO |
| Managed Accounts | One account per device (built-in or pre-created) | One account per device (built-in or automatically managed) |
| Account Provisioning | Requires manual creation or packaging scripts | Native Automatic Account Management creates the account (Windows 11 24H2+) |
| Post-Authentication Action | Not supported (manual resets only) | Automatic password reset and session logoff |
| Dedicated Event Logs | Application Log (event source AdmPwd) | Dedicated channel: Microsoft-Windows-LAPS/Operational |
Single Account Constraint: Windows LAPS architecturally manages only one local administrator account per endpoint. If your organization requires separate accounts for different administrative tiers, use Microsoft Entra role-based access control rather than configuring multiple LAPS policies on the same device.
Windows LAPS Architecture with Microsoft Intune
Understanding the architectural data flow prevents deployment misconfigurations across enterprise endpoints:
- Tenant Enablement: Microsoft Entra ID is configured to accept and store LAPS password metadata.
- Policy Assignment: Intune deploys an Account Protection policy using the native Windows LAPS Configuration Service Provider (CSP).
- Client Evaluation: The native Windows LAPS service on the endpoint evaluates the policy settings and checks the target administrator account.
- Password Generation: The operating system generates a new cryptographically randomized password matching the configured length and complexity requirements.
- Secure Cloud Backup: The client encrypts the password and uploads it to Microsoft Entra ID using the device identity certificate over TLS.
- Audit Logging: Entra ID logs the password update, and the local endpoint records success in the
Microsoft-Windows-LAPS/Operationalevent log.
Operating System Support Matrix and Prerequisites
Before deploying policies, verify that your client devices and tenant satisfy these baseline requirements:
| Component | Supported Editions and Versions | Operational Notes |
|---|---|---|
| Standard Windows LAPS | Windows 11 (all versions), Windows 10 (20H2, 21H2, 22H2 with KB5025221+) | Manages the built-in Administrator account or a pre-existing custom administrator account. |
| Automatic Account Management | Windows 11 version 24H2 or later, Windows Server 2025 or later | Creates, enables, and manages a custom administrator account automatically. Earlier OS versions ignore this setting. |
| Device Join State | Microsoft Entra joined or Microsoft Entra hybrid joined | Microsoft Entra registered (BYOD or Workplace Joined) devices are not supported. |
| Tenant Licensing | Microsoft Intune Plan 1 (M365 Business Premium, E3, E5, EMS E3/E5) | Microsoft Entra ID Free, P1, or P2 licenses support LAPS password storage. |
| Administrative Roles | Intune Administrator, Cloud Device Administrator | Password recovery requires Cloud Device Administrator or specific permissions. Helpdesk Administrator cannot view cleartext passwords in Entra ID by default. |
Step 1: Enable Windows LAPS in Microsoft Entra ID
Microsoft Entra ID requires an administrative opt-in before accepting and storing LAPS passwords from managed endpoints. Enabling this tenant setting is the first required step.
- Sign in to the Microsoft Entra admin center (entra.microsoft.com).
- In the left navigation menu, expand Devices and select All devices.
- Under the Manage section, click Device settings.
- Locate the setting labeled Enable Microsoft Entra Local Administrator Password Solution (LAPS).
- Toggle the switch to Yes.
- Click Save at the top of the page.
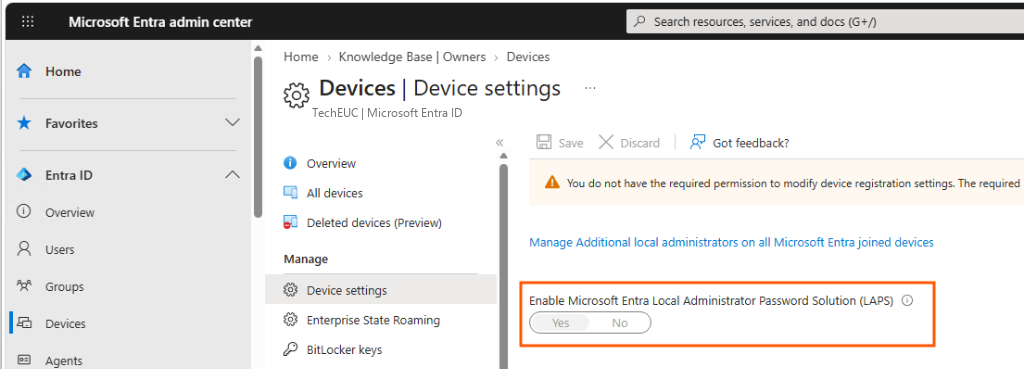
Warning: If you skip this step, client devices receiving the Intune policy will attempt to upload their generated passwords to Entra ID and encounter error code 0x80072EE7 or Event ID 10025 (Failed to discover Entra tenant capabilities).
Step 2: Create the Windows LAPS Policy in Microsoft Intune
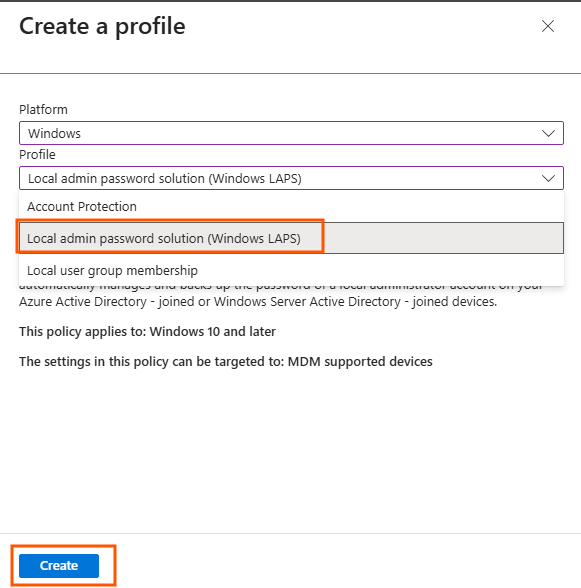
Intune manages Windows LAPS through the Endpoint Security Account Protection configuration service provider (CSP).
- Sign in to the Microsoft Intune admin center (intune.microsoft.com).
- Go to Endpoint security > Account protection.
- Click Create Policy at the top of the table.
- Set Platform to Windows (or Windows 10 and later).
- Set Profile to Local admin password solution (Windows LAPS).
- Click Create.
In the Basics tab, provide a descriptive policy name and description:
- Name:
TechEUC - Microsoft Windows LAPS(example lab policy name) - Description:
Windows LAPS Configuration policy in Microsoft Intune for TechEUC devices.
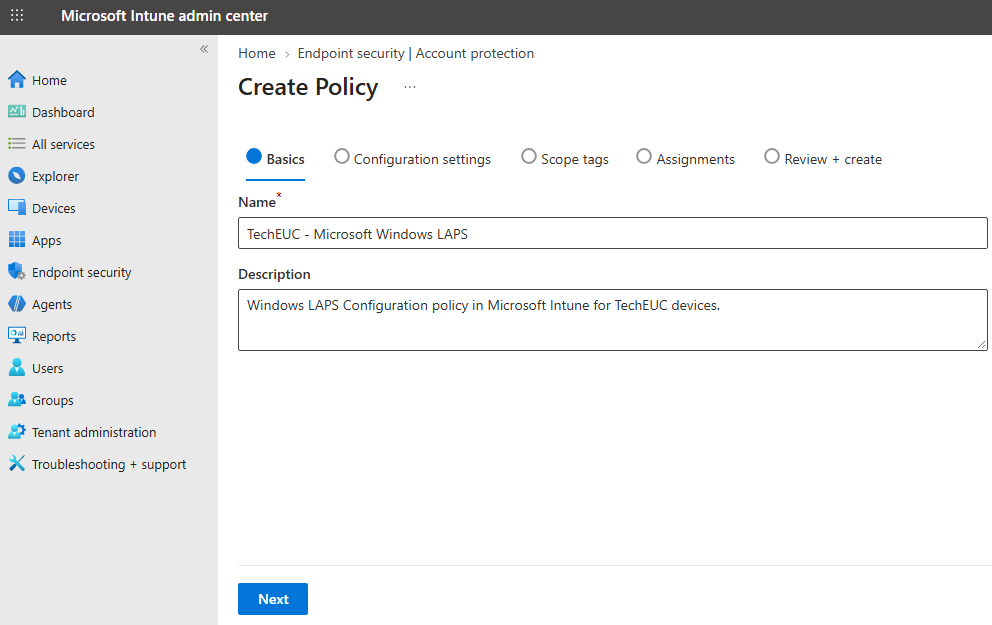
Click Next to proceed to Configuration settings.
Step 3: Configure LAPS Policy Settings and Automatic Account Management
The configuration settings tab defines how passwords are generated, rotated, and backed up. Windows LAPS includes native Automatic Account Management, which can provision a new custom local administrator account automatically on target workstations running Windows 11 version 24H2 or later.
In our lab demonstration, we configure the policy to manage a custom account named ITAdmin:
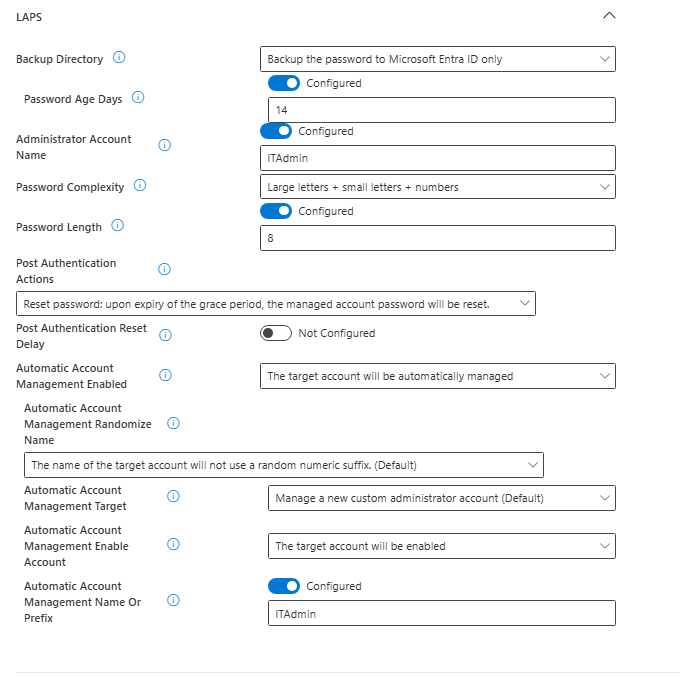
Review the purpose and enterprise recommendations for each setting configured in this profile:
| Setting | Lab Example Setting | Enterprise Recommendation | Technical Function |
|---|---|---|---|
| Backup Directory | Backup the password to Microsoft Entra ID only | Microsoft Entra ID only | Directs client endpoints to encrypt and upload password metadata directly to Microsoft Entra ID. |
| Password Age Days | 14 | 14 to 30 days | Specifies the rotation interval. The Windows LAPS client will generate a new randomized password every 14 days. |
| Administrator Account Name | ITAdmin | Custom account or blank (RID 500) | Specifies the name of the local account whose password will be managed. Leaving this blank defaults to the built-in Administrator account. |
| Password Complexity | Large letters + small letters + numbers | All 4 character classes where supported | Enforces high character entropy, preventing dictionary and credential stuffing attacks. |
| Password Length | 8 | 16 or more characters | Configures password length. While 8 characters was used in this test lab, 16 or more characters is recommended for enterprise production baselines. |
| Post Authentication Actions | Reset password upon grace period expiry | Reset password and log off account | After an administrator authenticates with the LAPS credential, Windows starts a grace period timer. When the timer expires, the password resets automatically. |
| Automatic Account Management Enabled | The target account will be automatically managed | Enabled (Windows 11 24H2+ only) | Instructs the Windows LAPS OS client to manage the local account lifecycle directly without third-party scripts. |
| Automatic Account Management Target | Manage a new custom administrator account | Manage custom administrator account | Windows LAPS automatically creates the local administrator account if it does not already exist on the client endpoint. |
| Automatic Account Management Enable Account | The target account will be enabled | The target account will be enabled | Ensures the target administrator account is set to active and unblocked for immediate troubleshooting use. |
| Automatic Account Management Name Or Prefix | ITAdmin | Standardized enterprise prefix | Defines the exact account name created and maintained by the Windows LAPS service. |
Technical Analysis: Automatic Account Management in Windows 11 24H2. In earlier Windows versions, administrators had to deploy a separate PowerShell script or Win32 app to create a custom local administrator account before LAPS could manage it. With Automatic Account Management enabled on Windows 11 24H2 or Windows Server 2025, the operating system creates the account, adds it to the local Administrators group, enables it, and rotates its password entirely through native kernel calls.
Click Next. On the Scope tags tab, select your required scope tag (or keep Default) and click Next:
Step 4: Assign Policy and Prevent Policy Conflicts
On the Assignments tab, assign the policy to your targeted Windows device group (e.g. Pilot-Windows-Endpoints or All Windows Devices). Complete the wizard on the Review + create tab and click Save.
Avoiding Conflicting LAPS Policies in Enterprise Environments
Policy conflicts cause client-side processing failures and must be prevented during deployment planning:
- Hybrid Azure AD Joined Devices: If a device receives legacy GPO settings (pointing to on-premises AD via AdmPwd) and modern Intune CSP settings (pointing to Entra ID), the client machine encounters policy conflicts. Filter out legacy LAPS GPOs for Intune-managed hybrid endpoints using WMI or security group scoping.
- Multiple Intune Profiles: Do not assign multiple Account Protection LAPS policies to the same device. If conflicting settings target an endpoint, the device flags the profile as in conflict in the Intune monitoring blade.
Step 5: Triggering Policy Sync and Client Evaluation
By default, Intune client devices check in for policy updates every 8 hours. To apply the Windows LAPS policy immediately on a test machine:
- On the client endpoint, open Settings > Accounts > Access work or school.
- Select the connected tenant account, click Info, and click Sync.
- Alternatively, open PowerShell as Administrator and run:
Invoke-LapsPolicyProcessing
The Invoke-LapsPolicyProcessing cmdlet forces the Windows LAPS background engine to query MDM policies, create or locate the target account (ITAdmin), generate an initial password, and write the credential to Microsoft Entra ID.
Step 6: Validating LAPS Policy on the Client Device
Before checking administrative web consoles, verify that the Windows endpoint processed the policy successfully using local diagnostic tools.
1. Inspecting the Windows Registry
When Intune applies the Account Protection policy via Policy CSP, settings are written directly to the Windows Registry under:
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Policies\LAPS
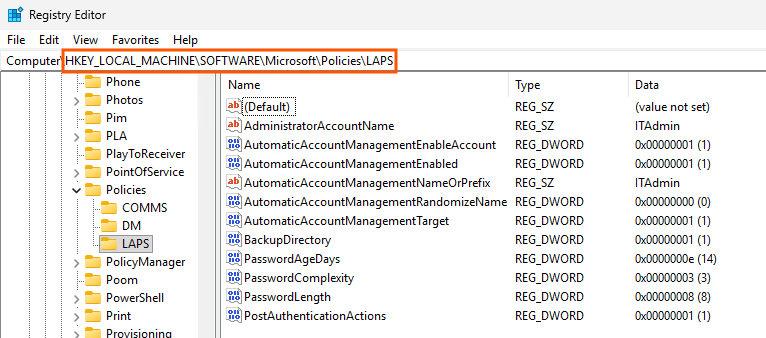
You can also query this key via PowerShell to automate deployment validation across endpoints:
Get-ItemProperty -Path "HKLM:\SOFTWARE\Microsoft\Policies\LAPS"
The registry confirms that AdministratorAccountName is set to ITAdmin, BackupDirectory is set to 1 (Microsoft Entra ID), PasswordAgeDays is set to 14 (hex 0xe), PasswordLength is set to 8, and AutomaticAccountManagementEnabled is active.
2. Checking the Dedicated Event Viewer Channel
Modern Windows LAPS writes detailed processing diagnostics to its dedicated Windows Event Log channel:
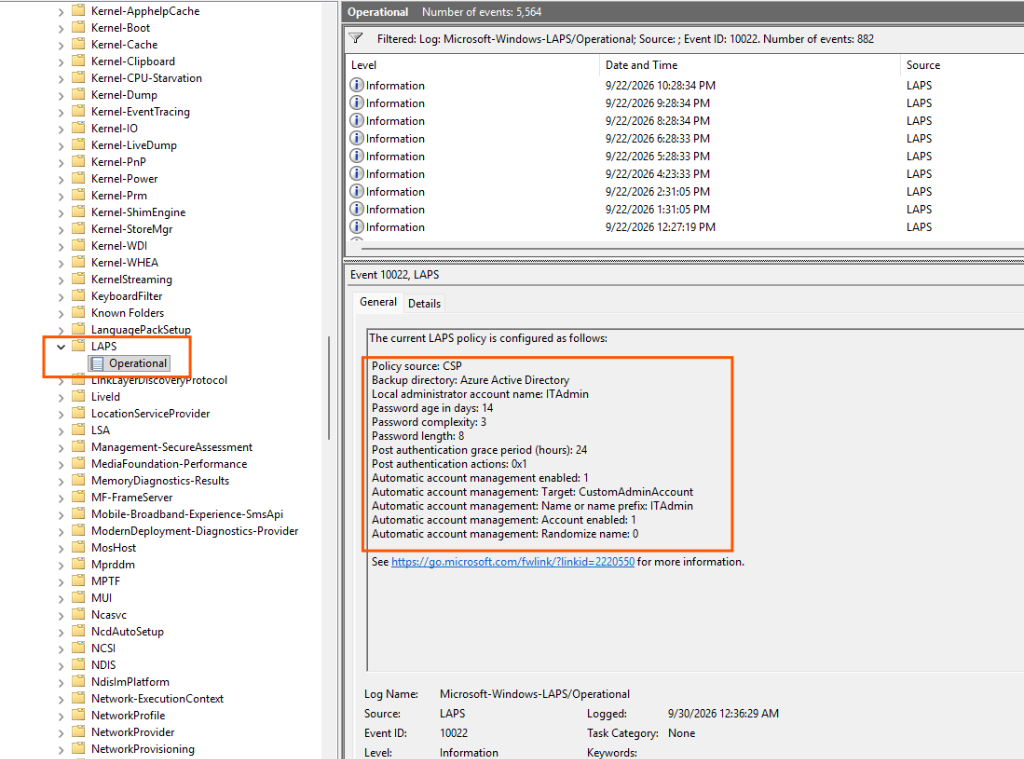
Applications and Services Logs > Microsoft > Windows > LAPS > Operational
Windows LAPS Event IDs Explained (Operational Runbook)
When monitoring deployments or diagnosing failures, review these specific Event IDs in the Microsoft-Windows-LAPS/Operational log:
Event ID 10003: Policy Processing Initiated
Indicates that the Windows LAPS background engine started a scheduled or manual policy processing cycle. This event logs the triggering reason (such as system startup, timer expiry, or manual invocation via Invoke-LapsPolicyProcessing).
Event ID 10004: Policy Processing Succeeded
Confirms that Windows LAPS completed evaluation without errors. The managed local account was verified or updated, and the current password status is compliant with policy settings.
Event ID 10005: Policy Processing Failed (Common HRESULT Errors)
Logged when LAPS encounters an execution failure. Always inspect the specific HRESULT error code in the event body:
0x80070005 (E_ACCESSDENIED):The LAPS service lacks permissions to update the account password or write to the target directory.0x80072EE7 (WININET_E_NAME_NOT_RESOLVED):Client cannot resolve Entra ID endpoints due to DNS or network disconnects.0x80070032 (ERROR_NOT_SUPPORTED):The operating system does not support the requested feature (such as Automatic Account Management requested on Windows 10 or Windows 11 versions prior to 24H2).
Event ID 10013: Local Administrator Account Not Found
Occurs when the account specified in AdministratorAccountName does not exist on the local workstation, and Automatic Account Management is either disabled or unsupported on the operating system. Verify the exact account name or enable Automatic Account Management on Windows 11 24H2+.
Event ID 10022: Policy Configuration Parameters Evaluated
Details the exact policy parameters parsed by the Windows LAPS engine from the CSP or GPO source. This provides immediate proof of which settings were delivered to the endpoint:
The current LAPS policy is configured as follows:

Policy source: CSP
Backup directory: Azure Active Directory
Local administrator account name: ITAdmin
Password age in days: 14
Password complexity: 3
Password length: 8
Post authentication grace period (hours): 24
Post authentication actions: 0x1
Automatic account management enabled: 1
Automatic account management: Target: CustomAdminAccount
Automatic account management: Name or name prefix: ITAdmin
Automatic account management: Account enabled: 1
Automatic account management: Randomize name: 0
Event ID 10025: Entra ID Discovery or Communication Failed
Logged when the endpoint cannot communicate with the Microsoft Entra LAPS service. This typically indicates that the tenant toggle Enable Microsoft Entra Local Administrator Password Solution (LAPS) is set to No, or outbound network access to enterpriseregistration.windows.net is blocked by an enterprise firewall.
Event ID 10029: Local Administrator Password Successfully Backed Up
The definitive indicator of deployment success. Confirms that the newly generated password for the managed local administrator account was encrypted and committed to Microsoft Entra ID.
Step 7: Retrieving the Local Administrator Password
Once the endpoint logs Event ID 10029, administrators can retrieve the cleartext password using three separate methods.
Method 1: In the Microsoft Intune Admin Center
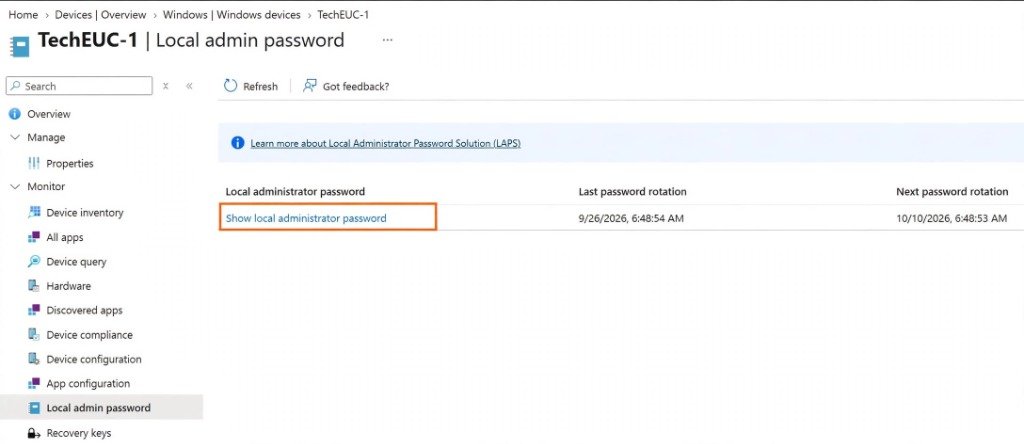
- Go to Devices > Windows > select your target device (such as
TechEUC-1in our lab). - In the device sub-menu under Monitor, click Local admin password.
- Click Show local administrator password.
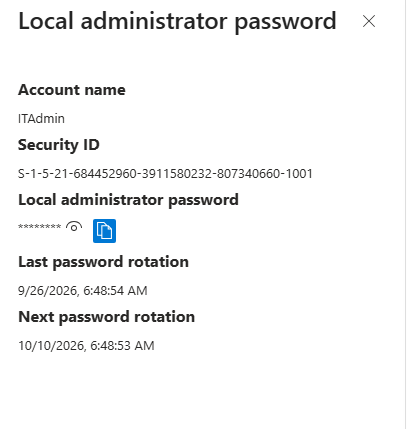
Intune opens a flyout pane displaying the managed account name (ITAdmin), Security ID (SID), cleartext password, last rotation timestamp, and the next scheduled rotation date:
Method 2: In the Microsoft Entra Admin Center
- Sign in to the Microsoft Entra admin center (entra.microsoft.com).
- Navigate to Devices > All devices.
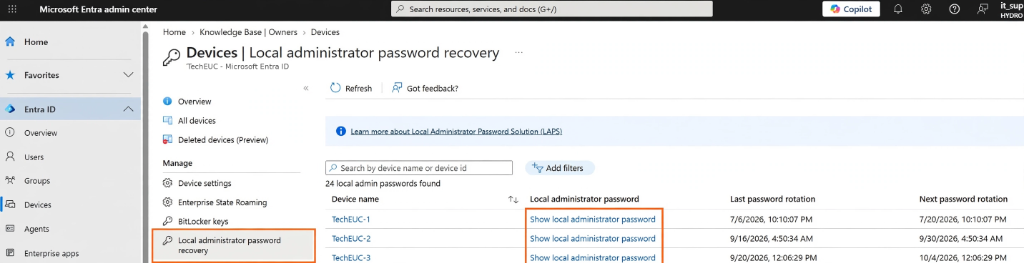
- Under the Manage section in the left menu, click Local administrator password recovery.
- Find your device (e.g.
TechEUC-1,TechEUC-2, orTechEUC-3) in the inventory table. - Click Show local administrator password.
Method 3: Using Microsoft Graph PowerShell
Helpdesk and automation teams can retrieve passwords programmatically using the Microsoft Graph PowerShell SDK:
Connect-MgGraph -Scopes "DeviceLocalCredential.Read.All"
$device = Get-MgDevice -Filter "displayName eq 'TechEUC-1'"
Get-MgDeviceLocalCredential -DeviceId $device.Id | Select-Object -ExpandProperty Credentials
Security Auditing: Every time an administrator views a LAPS password in Intune, Entra ID, or through PowerShell, Microsoft Entra ID creates an entry in the Audit logs with activity Read MS-Mcs-AdmPwd (LAPS) password, recording the user principal name, device ID, and timestamp.
Step 8: On-Demand Remote Password Rotation
If a technician finishes a troubleshooting session and you want to rotate the credential immediately without waiting for the 14-day cycle or the post-authentication timer:
- In the Microsoft Intune admin center, navigate to Devices > Windows > select your device.
- In the top toolbar, click the three horizontal dots (…) to reveal more remote actions.
- Click Rotate local admin password.
- Confirm the prompt. Intune sends an immediate push notification to the client endpoint to generate a new password and sync it to Entra ID.
Windows LAPS Role-Based Access Control (RBAC) and Security
To enforce zero trust and least privilege, do not assign Global Administrator roles simply to read local admin passwords. Microsoft Entra ID and Intune distinguish between device management and credential recovery:
- Intune RBAC Permissions: Technicians need Managed Devices > Read and Managed Devices > Query Local Administrator Password permissions. This is included in the Endpoint Security Manager and Helpdesk Operator roles in Intune.
- Entra ID Role Boundaries: Cloud Device Administrator and Global Administrator have native permissions to read cleartext LAPS passwords in Entra ID. Helpdesk Administrator cannot view cleartext LAPS passwords by default.
- Custom Entra ID Role for Tier-1 Support: Create a dedicated custom role scoped to devices with only the
microsoft.directory/deviceLocalCredentials/password/readpermission. This allows helpdesk technicians to view LAPS passwords without granting broad directory administrative rights.
Frequently Asked Questions (Windows LAPS in Intune FAQ)
What is Windows LAPS?
Windows Local Administrator Password Solution (Windows LAPS) is a native Windows feature that automatically manages, rotates, and backs up the password of a local administrator account to Microsoft Entra ID or Active Directory.
Does Windows LAPS require Microsoft Intune?
No. While Microsoft Intune provides centralized cloud policy management through the Account Protection CSP, Windows LAPS can also be managed using Group Policy Objects (GPO) in on-premises Active Directory environments.
Does Windows LAPS support Microsoft Entra joined devices?
Yes. Microsoft Entra joined devices natively support modern Windows LAPS policies delivered via Intune, with passwords encrypted and backed up directly to Microsoft Entra ID.
Does Windows LAPS support Hybrid Azure AD joined devices?
Yes. Hybrid Azure AD joined devices support Windows LAPS with the option to back up passwords either to Microsoft Entra ID or to on-premises Active Directory.
Does Windows LAPS work with Microsoft Entra registered devices?
No. Microsoft Entra registered devices (such as personal BYOD or Workplace Joined machines) are not supported by Windows LAPS.
Can Windows LAPS create a local administrator account automatically?
Yes, through Automatic Account Management. When configured in Intune, the operating system can automatically provision, enable, and manage a new custom local administrator account without pre-install scripts.
What Windows versions support Automatic Account Management?
Automatic Account Management requires Windows 11 version 24H2 or later, or Windows Server 2025 or later. Earlier Windows 10 and 11 versions support standard Windows LAPS but cannot automatically create accounts.
How often does Windows LAPS rotate passwords?
Password rotation intervals are determined by your policy settings, ranging from 1 to 365 days. Enterprise baselines typically specify rotation every 14 to 30 days.
Where is the Windows LAPS password stored in Microsoft Entra ID?
LAPS passwords are stored as encrypted device credential objects associated with the device entity in Microsoft Entra ID, retrievable through the Entra portal, Intune portal, or Microsoft Graph API.
How do I force Windows LAPS policy processing immediately?
Open PowerShell as Administrator on the client device and execute Invoke-LapsPolicyProcessing to trigger an immediate policy evaluation and password backup.
What is Windows LAPS Event ID 10029?
Event ID 10029 confirms that the local administrator password was successfully generated, encrypted, and backed up to Microsoft Entra ID.
What is Windows LAPS Event ID 10025?
Event ID 10025 indicates that the client device failed to discover Entra ID LAPS capabilities, typically caused by the tenant setting being disabled or network connectivity issues.
Can Windows LAPS completely replace legacy Microsoft LAPS?
Yes. Modern Windows LAPS completely replaces legacy Microsoft LAPS (AdmPwd.dll), offering native OS integration, cloud backup to Entra ID, and automatic post-authentication resets.
Can Windows LAPS manage multiple local administrator accounts on one machine?
No. Windows LAPS is designed to manage exactly one local administrator account per endpoint.
Topic Cluster: Related Intune and Endpoint Engineering Runbooks
Explore related enterprise configuration runbooks and troubleshooting guides across the TechEUC endpoint management cluster:
- Fix Intune Error 0x87D1041C: App Not Detected After Installation
- Intune Management Extension (IME) Log Files Troubleshooting Guide
- Force Update Microsoft Defender Antivirus with PowerShell & Intune
- How to Setup Windows Autopilot Step-by-Step Complete Guide
Official Microsoft Documentation References
For official architectural specifications and API documentation, consult the following Microsoft Learn resources:
- Microsoft Learn: Windows LAPS Overview in Microsoft Intune
- Microsoft Learn: Deploy Windows LAPS policy with Microsoft Intune
- Microsoft Learn: Windows LAPS Policy CSP and Registry Settings
- Microsoft Graph API: directory deviceLocalCredentials Reference
Need Enterprise Endpoint Security Engineering?
Implementing zero-trust endpoint access and securing local administrator privileges across thousands of Windows workstations requires disciplined policy design. If your organization is transitioning from legacy GPO solutions to modern Microsoft Intune architecture, TechEUC provides specialized enterprise infrastructure engineering. Reach out through our Contact Page to collaborate on your endpoint security initiatives.